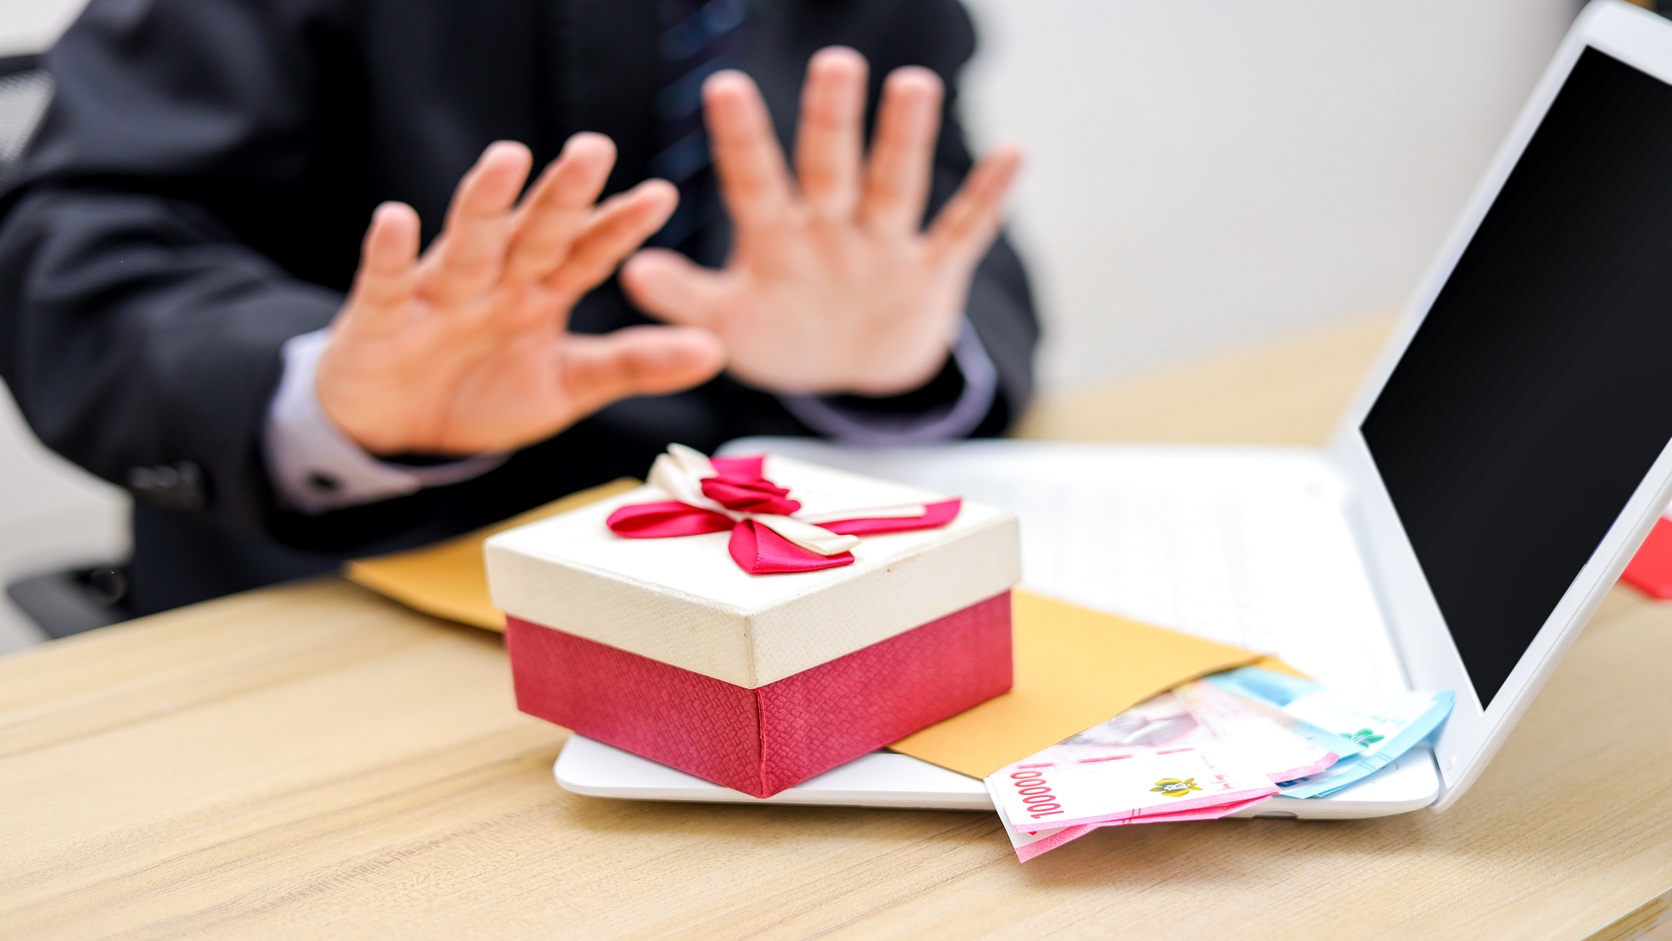
ISO 37001 certification assesses an anti-bribery management system. Its purpose is to support an organisation’s efforts to prevent, detect and respond to bribery through proportionate management arrangements. The practical question is what happens when a commercial opportunity, intermediary, payment or personal relationship creates pressure to overlook a concern.
ISO 37001:2025 is the current published edition, confirmed by ISO’s standard record. A certificate is not proof that bribery has never occurred, and it does not provide immunity from investigation or liability. Buyers should examine the certified boundary and the organisation’s relevant controls rather than treating the certificate as a declaration of innocence or a guarantee about every transaction.
Start with the decisions most exposed to pressure
Map how business is won, purchases are approved, permits are sought and third parties act for the organisation. Consider interactions in public, private and not-for-profit settings. Bribery risk can arise through direct activity or through business associates. A system focused only on one category of employee may overlook important routes through which an improper benefit could be offered or received.
Ask where personal discretion, urgent deadlines, opaque payments or incentives create difficulty. The answer should reflect the organisation’s actual markets and activities. Avoid assuming that a large customer is low risk or that a small payment is automatically acceptable. The relevant law, purpose and circumstances require competent consideration, and commercial convenience should not settle the decision.
Make the certification boundary understandable
Identify the legal entities, locations, activities and organisational relationships intended for assessment. Clarify how subsidiaries, joint ventures, agents and other business associates relate to the management system. An organisation may have differing degrees of control or influence; the public scope should not imply coverage that the assessment does not establish.
For procurement, compare the certificate with the entity entering your contract. Ask whether the relevant business activity is within scope and what assurance is available about important intermediaries. Do not infer that every related company has been assessed because a corporate parent has a certificate. Scope questions can be asked without requesting confidential investigation details or personal information that the buyer has no legitimate need to receive.
Assess bribery risk before prescribing the same control everywhere
A risk assessment should help choose appropriate measures for the organisation’s circumstances. Consider transactions, business relationships, decision authority and relevant external conditions. Record the reasoning behind priorities and reassess when circumstances change. A generic country score alone cannot explain the risk in a specific relationship or payment arrangement.
Give operational managers a practical role. They often know how an intermediary was selected, why a commission is unusual or whether an invoice description matches the service. Combine that knowledge with compliance expertise and appropriate independence. A spreadsheet that labels every relationship acceptable without investigation provides little support for a defensible decision, even if all required fields are complete.
Use due diligence to resolve questions
Due diligence should address the risk and the decision being considered. Establish why a business associate is needed, what service it will provide, how it was selected and whether proposed payment arrangements make sense. Investigate material inconsistencies rather than treating a completed questionnaire as an automatic approval.
Keep the process proportionate and respect privacy and other applicable requirements. Some relationships warrant more detailed enquiries and ongoing review than others. Decide who may approve a relationship, when escalation is needed and what happens if sufficient assurance cannot be obtained. Where legal interpretation is necessary, obtain qualified advice rather than relying on a certification claim or a general online article.
Follow one decision through the control system
The following original table supports discussion between procurement, finance and compliance. It is not a legal safe harbour or a prescribed ISO risk rating.
|
Decision |
Question that deserves an answer |
Evidence to examine |
|
Appointing an intermediary |
What legitimate service is required? |
Selection rationale, contract and proportionate diligence |
|
Approving a payment |
Does it match authorised work? |
Invoice, approval and service evidence |
|
Offering hospitality |
Is the purpose and context appropriate? |
Applicable rule, approval and accurate record |
|
Making a donation |
Who benefits and why now? |
Rationale, recipient checks and authority |
|
Responding to a concern |
Can the matter be assessed fairly? |
Protected reporting and controlled follow-up |
Test a recent transaction using the table. The strongest question is often whether different teams understood the same purpose, rather than whether each team completed its own form.
Connect financial and non-financial controls
Payments need appropriate authorisation, recording and supporting information. Commercial decisions also require controls: selection of partners, contract terms, procurement evaluations and exceptions can matter before finance sees an invoice. If an improper commitment has already been made, a final payment approval may be too late to prevent the underlying problem.
Examine unusual arrangements with appropriate care. A request for payment to an unrelated account, an unclear service description or pressure to avoid normal review may justify further enquiry. None of those features alone proves wrongdoing. The system should provide a way to investigate, decide and document the outcome without making unsupported accusations or encouraging staff to ignore concerns to meet a target.
Make reporting and follow-up credible
People need to know how to raise a concern and what protection and confidentiality arrangements apply. Consider language, access and whether a person feels safe reporting about a senior colleague or major customer. A reporting channel that exists only in a policy may not be usable for contractors or personnel without regular computer access.
Establish appropriate responsibility for evaluating concerns, conducting enquiries and acting on findings. Protect records and personal information. Avoid publicising allegations as though they were established facts. The US Department of Justice’s evaluation guidance offers a jurisdiction-specific perspective on whether compliance arrangements work in practice; it is not a global legal rule or a substitute for ISO 37001 requirements.
Leadership must address incentives and exceptions
A policy prohibiting bribery can be undermined by incentives that reward results regardless of how they are achieved. Ask what happens when an employee loses business by following the rules. Managers should understand the resources and authority needed for effective controls, including escalation where commercial leadership is involved in the proposed decision.
Review exceptions. Who may approve them, on what basis and with what safeguards? A system that routinely bypasses diligence for urgent transactions may leave its highest-pressure decisions least examined. Management needs useful information about outstanding concerns and control weaknesses, not simply the percentage of employees who completed online training.
A fictional example: a commission with an unclear purpose
Imagine a fictional exporter asked to appoint a new intermediary shortly before a major award. The proposed commission is substantial, while the contract describes only “market support.” Sales staff consider the appointment essential. Finance has no clear evidence of the services that will justify payment, and compliance receives the request after the commercial commitment is announced.
A practical response would establish the legitimate business need, perform appropriate diligence, review the payment basis and resolve concerns before approval. The fictional scenario illustrates control timing and shared responsibility. It does not allege misconduct by any real party, define a lawful commission rate or prescribe the legal outcome of an actual transaction.
Prepare evidence before seeking certification
Obtain the standard, agree scope and sponsorship, assess risks and establish proportionate arrangements. Assign the anti-bribery function appropriate responsibilities, competence and access. Train people for the risks in their roles, including purchasing, sales, finance and relevant leadership. Evidence should show how decisions are made, not just that a policy was circulated.
Use internal audits and management review to examine implementation, resources and effectiveness. Follow up nonconformities and evaluate corrective action. Ask CB Name about audit-team competence, confidentiality and how sensitive evidence will be reviewed. Confirm the exact issuer and relevant accreditation. Use the certification-body directory for discovery, then check approval independently rather than assuming it from the provider’s other services.
Consider cost and the certificate’s proper use
Costs can include internal time, diligence, specialist advice, training, reporting arrangements and external assessment. Existing legal and compliance duties remain relevant regardless of certification. A fixed certificate price cannot reveal whether the organisation has invested enough in the controls appropriate to its risk. Compare assessment proposals using the same scope information.
After certification, reassess significant changes in markets, transactions, ownership and relationships. Maintain accurate claims in tenders. For supplier certificate checks, follow the verification guide. The certificate can support a wider assurance decision, but specific concerns still require appropriate enquiry. It should not be used to dismiss credible evidence or to imply that regulatory authorities have approved every business practice.
Test whether a concern can reach an independent decision
Choose a hypothetical concern involving an important customer or a senior manager. Ask how it would be received, who would assess it and how conflicts of interest would be managed. Do not use real personal allegations in an open training exercise. The purpose is to test the route and responsibilities without exposing confidential information.
Examine practical access. A reporting channel may be difficult to use for people working remotely, speaking another language or employed by a business associate. Consider whether the arrangements communicate appropriate protections and realistic confidentiality limits. Promising absolute secrecy can be misleading where investigation or law requires controlled disclosure.
Follow the hypothetical concern through to feedback and improvement. Who ensures records are protected? Who determines whether wider controls need review? How does leadership receive useful information without unnecessary personal detail? These questions help distinguish a functioning reporting process from a telephone number printed in a policy. Any actual concern should be handled through the appropriate procedures and with qualified advice where needed. The certificate does not settle the facts, and neither an allegation nor an absence of reports should be presented as conclusive evidence about the organisation's conduct.
References and information note
· ISO 37001:2025: anti-bribery management system requirements
· ISO: anti-bribery management systems overview
· ISO: practical implementation guide preview
· US Department of Justice: Evaluation of Corporate Compliance Programs
This global guide does not provide legal advice, determine wrongdoing or replace the standard. The example is fictional. Certification is not proof that no bribery exists. Refer factual clarifications to the contact page.